Find sanctioned and shadow agents.
RSA Agent ID Discover surfaces AI agents across your environment.
Know every agent operating in your environment.
Cross-environment
discovery.
Discover agents across identity, cloud, endpoint, and gateway.
Human ownership. Human accountability.
Tie every agent to a responsible human owner and managed lifecycle.
Insights—not just
inventory
Continuous analytics detail how your agents are evolving and highlight risks.
Breaches involving shadow AI cost organizations $400,000 more than the average incident.
You can’t secure what you don’t see.
One rogue agent is all it takes for financial services, government, and high-assurance organizations to lose control.
Continuous,
cross-environment discovery.
Discover finds agents—and what they can access—across identity, cloud, endpoint, and gateway.
Autonomy, meet accountability.
The agent identity crisis ends here.
Sovereign control
RSA Agent ID runs in the cloud, on-premises, or fully air-gaps. Agents stay secure even when they’re disconnected.
The new standard in agentic identity
Agentic security will be won or lost on identity. Learn the best practices high-assurance organizations need to keep it secure.
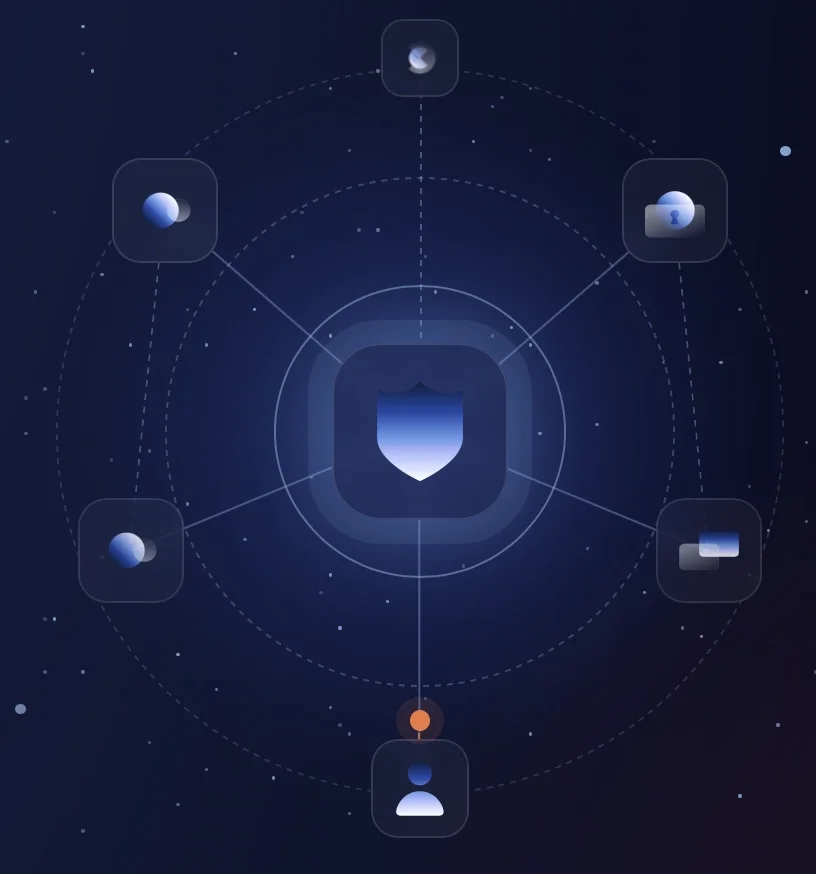
The agentic identity security platform for highly-regulated industries.
Know every agent. Control every action. Map regulatory evidence to ten industry frameworks with RSA Agent ID.
Agent ID
RSA® Agent ID discovers, secures, and governs agents throughout their lifecycle.
Agent ID Secure
RSA Agent ID Secure keeps humans in control of all agent actions.
Governance & Lifecycle
Complete identity governance and administration capabilities.
ID Plus
Deploy complete identity and access management capabilities across environments.
BRING AI OUT OF THE SHADOWS.
Ready to Discover Your Agents?
Contact RSA to speak with our experts and learn how Discover finds, inventories, and assigns human owners to every agent running in your environment.


 Included